Information Security Starts from the Top: The Crucial Role of Management in ISO 27001
For an Information Security Management System (ISMS) to be effective, leadership commitment is essential. In fact, ISO 27001 dedicates Clause 5 entirely to the role of top management in the success of the ISMS.
In particular, sub-clause 5.1 lists several areas where top management must play an active role:
- Strategic alignment. Information Security objectives must align with the strategic direction of the organization. It is the responsibility of top management to ensure that security goals not only mitigate risks but also support the broader business strategy.
- Integration into existing processes. A functioning ISMS is not a standalone system. Security controls and practices must be integrated into existing processes. Without buy-in from leadership, achieving this level of integration across departments is difficult.
- Budgeting. Mitigating security risks and pursuing ISO 27001 certification can involve significant financial investments. Top management must recognize their value and allocate the necessary budget to support both the annual certification process and ongoing ISMS operations.
- Company-wide awareness and responsibility. Information security is not just the domain of IT. A secure system requires that every person of every department—from Human Resources to Facilities Management and Legal—is aware and acts responsibly. Top management is responsible for supporting departmental managers’ role in Information Security and for fostering a culture of security awareness across the company.
- Ongoing improvement. Top management is responsible for the achievement of ISMS objectives and for promoting continuous improvement.
As a certification body, one aspect our auditors look for when assessing compliance with Clause 5 is management's involvement during the audit process. “We understand that senior leaders are very busy people with lots of commitments and priorities, so when they take the time to get involved in the opening and closing meetings, it demonstrates to us that they are committed and understand the importance of a strong ISMS,” says NSF Information Security audit manager Megan Turner.
Are you ready to strengthen your Information Security system? Get in touch with NSF to start your ISO/IEC 27001 certification process.
ISO/IEC 27001: Information Security Management
How NSF Can Help You
What’s New with NSF
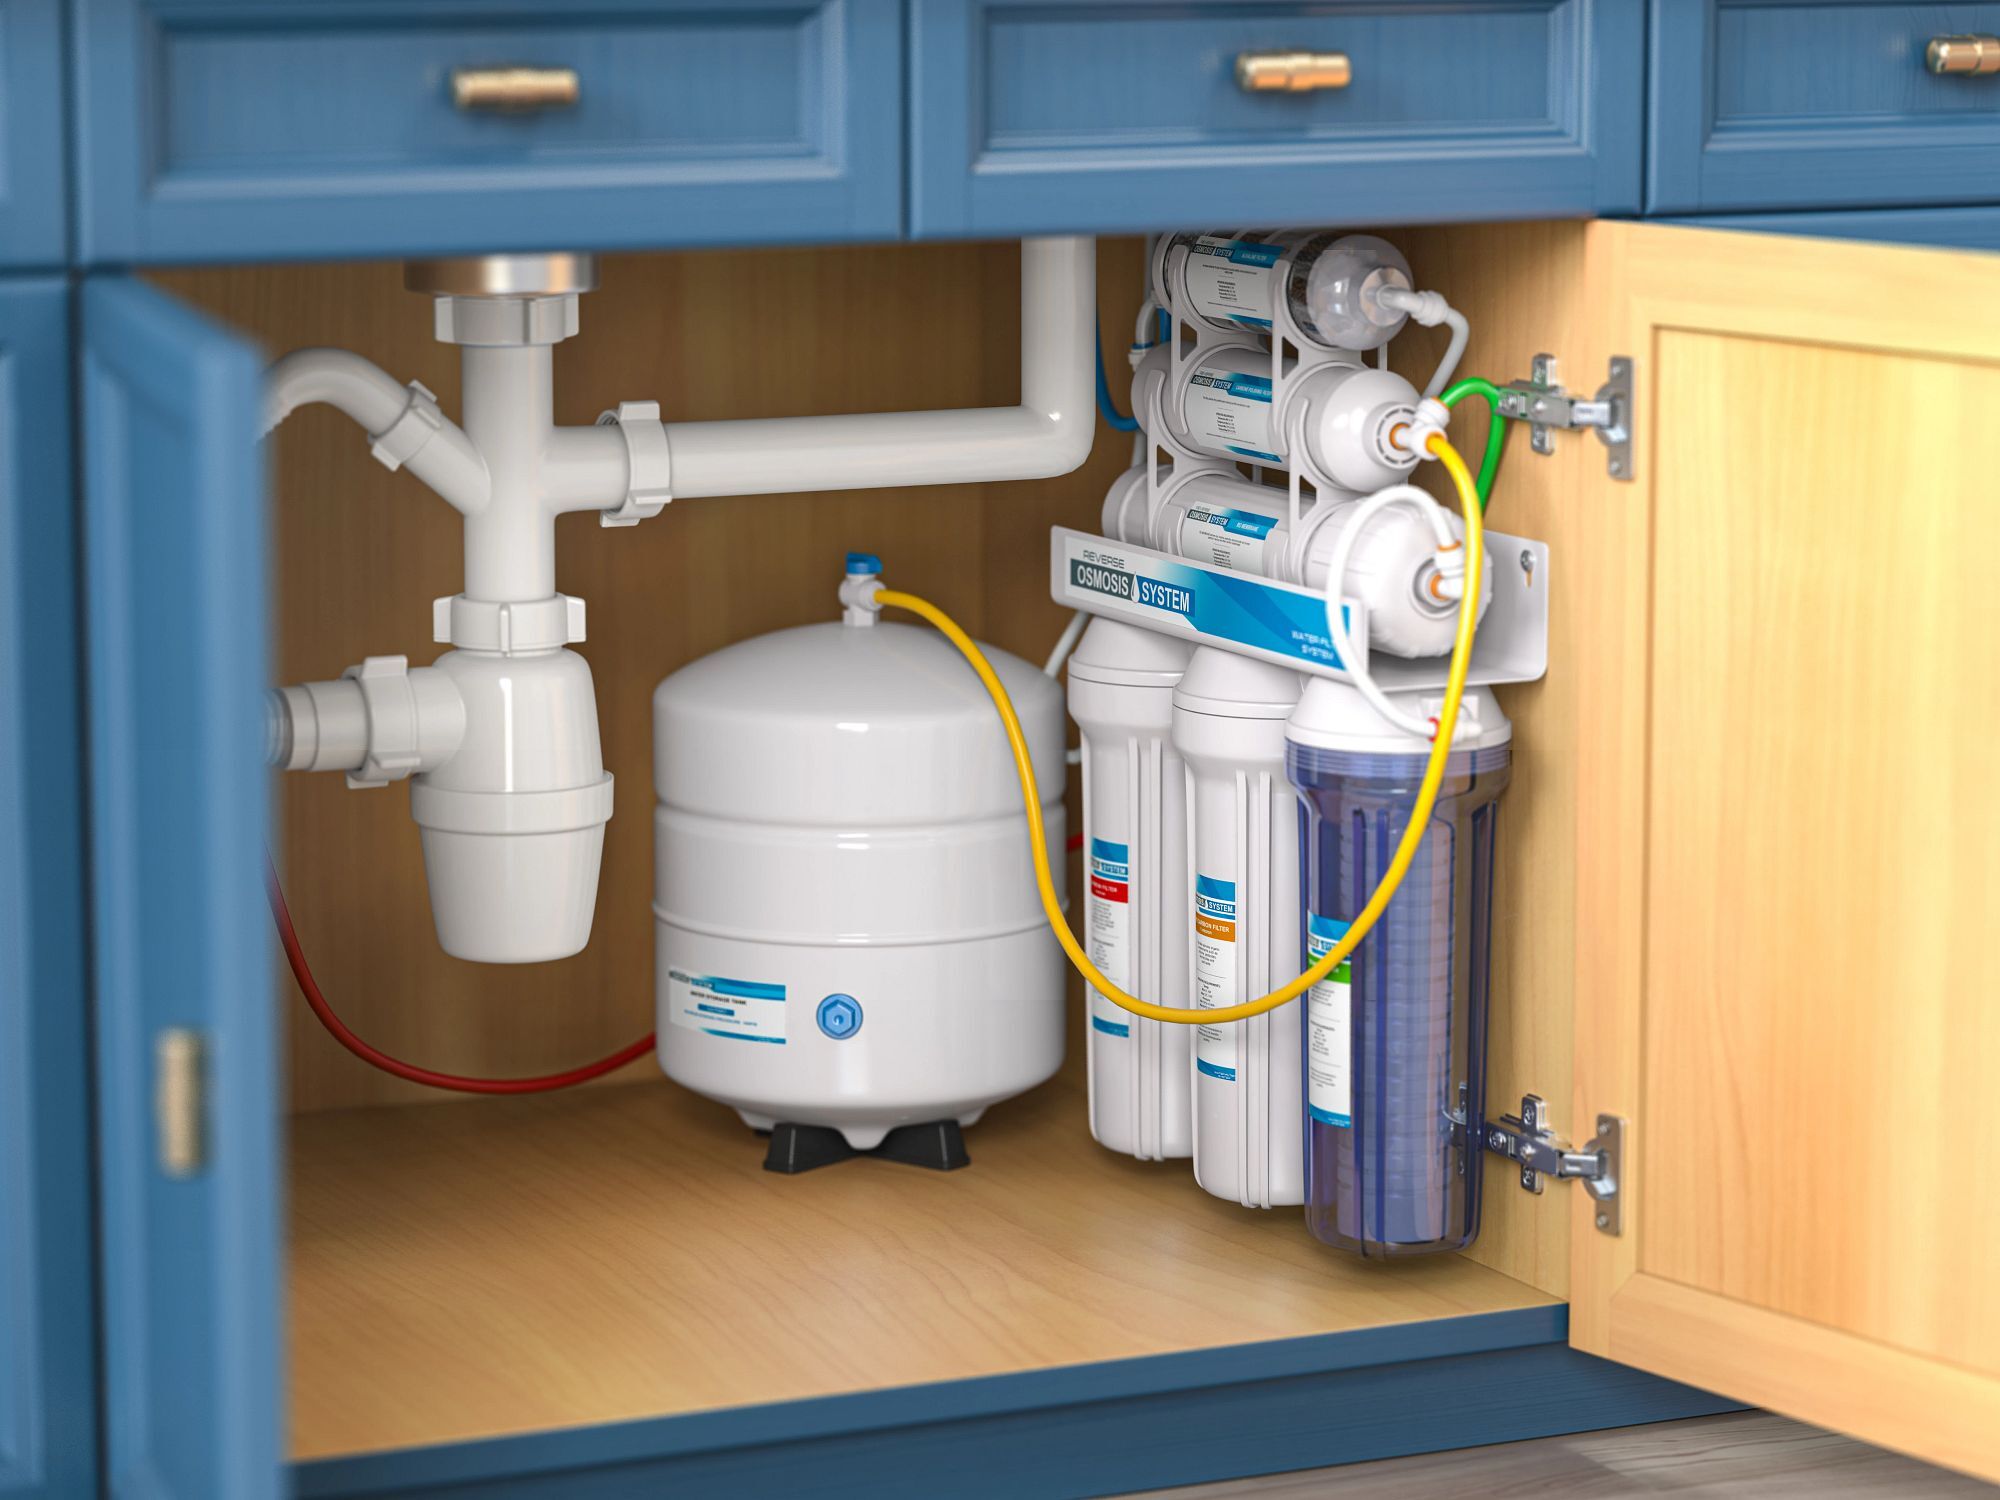
NSF Launches Protocol 549 for Glyphosate Reduction Claims
October 14, 2026P549 is the first standard globally that validates glyphosate reduction performance of water filtration systems and products.
NSF Welcomes Nicole Parent Haughey to Board of Directors
September 10, 2026NSF's appointment of Nicole supports the organisation's continued focus on long-term growth and transformation.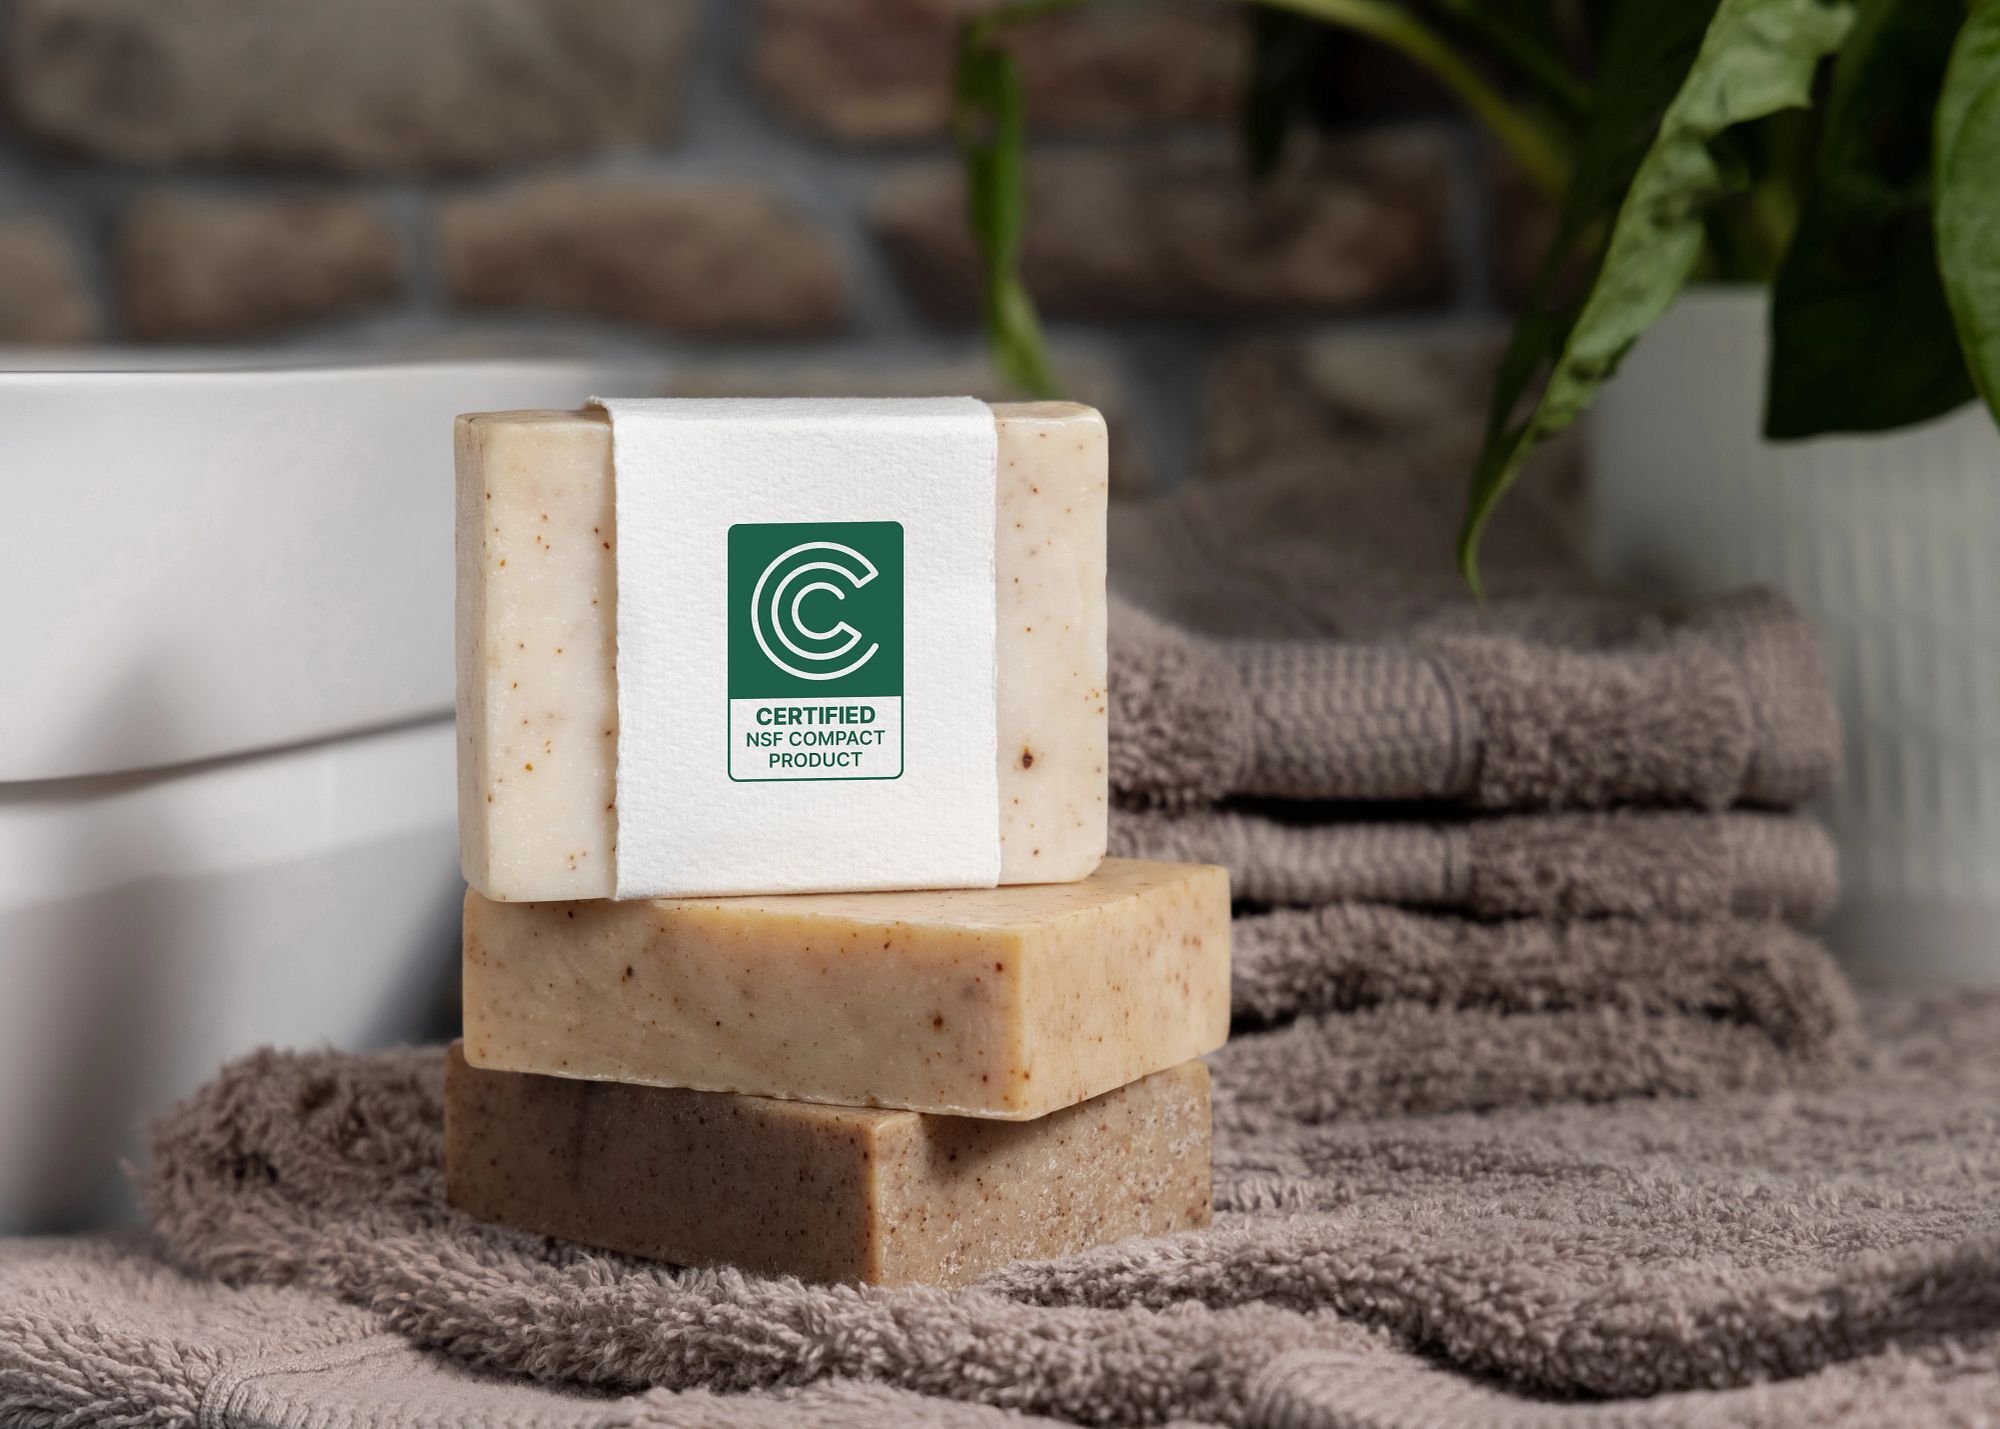
NSF Launches Independent Certification Standard for Compact Products
August 25, 2026New third-party certification verifies products cutting materials and shipping impacts while maintaining safety and performance.