The New CMMC Requirements: It’s Not Abstract Art
For some small and medium companies that do business with the U.S. Department of Defense (DoD), the new CMMC requirements may look a bit like abstract art: Lots of random shapes and squiggly lines, but how to make sense of all the different patterns?
Tony Giles is an information security expert with NSF International Strategic Registrations (NSF-ISR), and he understands the abstract art analogy well. In fact, when he was finishing high school, he thought about going to art school. “I actually draw and I enjoy art quite a bit,” Giles says. “Abstract art for me is along the lines of organized chaos. For the artist, it’s a masterpiece, but for some people, it’s just scribbles.”
Giles serves as NSF-ISR’s information security business lead, lead auditor and CMMC provisional assessor. His goal is to assess and help DoD suppliers make sense of the CMMC information security “abstract patterns.”
CMMC stands for Cybersecurity Maturity Model Certification. It’s the new, mandatory information security requirement announced by the Defense Department in 2020 that requires all 350,000-plus department contractors and their supply chains to be fully audited and certified by the end of 2025. Starting January 1, 2026, contracts must specify in writing that the company is in full compliance with the DoD requirement.
“It’s the first ever mandated information security standard,” Giles says. “One the defense industrial base (DIB) and the Department of Defense are extremely interested in. And they want to see organizations meet those requirements.”
When Giles says “mandated,” he means exactly that. Any DoD supplier not audited and certified for compliance with CMMC information security standards by the end of 2025 will lose the right to do business with the department. For a good number of small to medium size contractors, that loss of essential federal government business could mean the difference between staying in business and being forced to close their doors. That’s the cold, hard reality of CMMC.
Giles and his team of auditors provide assessments to DoD contractors to ensure they are in compliance by the program’s end-of-December 2025 deadline. The team works with a wide variety of companies that are at different stages of the information security journey.
“Some are extremely technical and know exactly what to do and how to implement the requirements,” he says. “Others need more guidance, and we are here to provide the right help. We make sure everyone understands the process and that compliance is not so complicated. It's just certain things that have to be in place and things we have to check.”
Giles wants to demystify security and make it relatable, so that businesses of all sizes can implement the necessary security controls mandated under CMMC. “I want to be able to describe the program and have organizations understand exactly what they need to implement. And put it into terms that make sense for small businesses, medium-sized businesses and even large-scale organizations,” he says.
Giles has been with NSF-ISR for about 15 years. He got started in information security early on when NSF-ISR was offering an information security course to staff as part of an ISO 27001 certification program. In fact, Giles became one of the first auditors for ISO 27001, the recognized international standard on how to manage information security.
“We work with so many different kinds of customers,” Giles says. “I think that's the most rewarding part. You can work with a software firm one day and a manufacturing firm the next day. And then a small business on the defense side and a huge Fortune 100 company, all in the same week. The variety of customers is rewarding.”
That variety of clients provides a different pattern to observe and assess during each visit, which is not that different from appreciating the lines and patterns of an abstract work of art. What’s the overall pattern? What are the individual pieces? What pieces might be missing? And, most importantly, how does everything fit together into one, cohesive whole?
Ready to Begin the Process?
Resources
Helping Clients Ensure Information Security
Information security expert Rhia Dancel fell in love with science as a child when her parents gave her a microscope. Now she helps clients ensure the security of their information.
Cybersecurity Maturity Model Certification (CMMC) Terminology and FAQs
ArticleLearn the specific terms associated with Cybersecurity Maturity Model Certification and get answers to some frequently asked questions about the program.
Cybersecurity Maturity Model Certification (CMMC) Assessments and What You Need to Know
Join Tony Giles, Rhia Dancel and Don McFarland as they discuss what management systems certified organizations need to know in preparation for CMMC assessments. The team covers CMMC levels 1-3, who is assessing, what Level 1 CMMC covers, what to expect in a CMMC assessment and a few new key updates.
How NSF Can Help You
What’s New with NSF
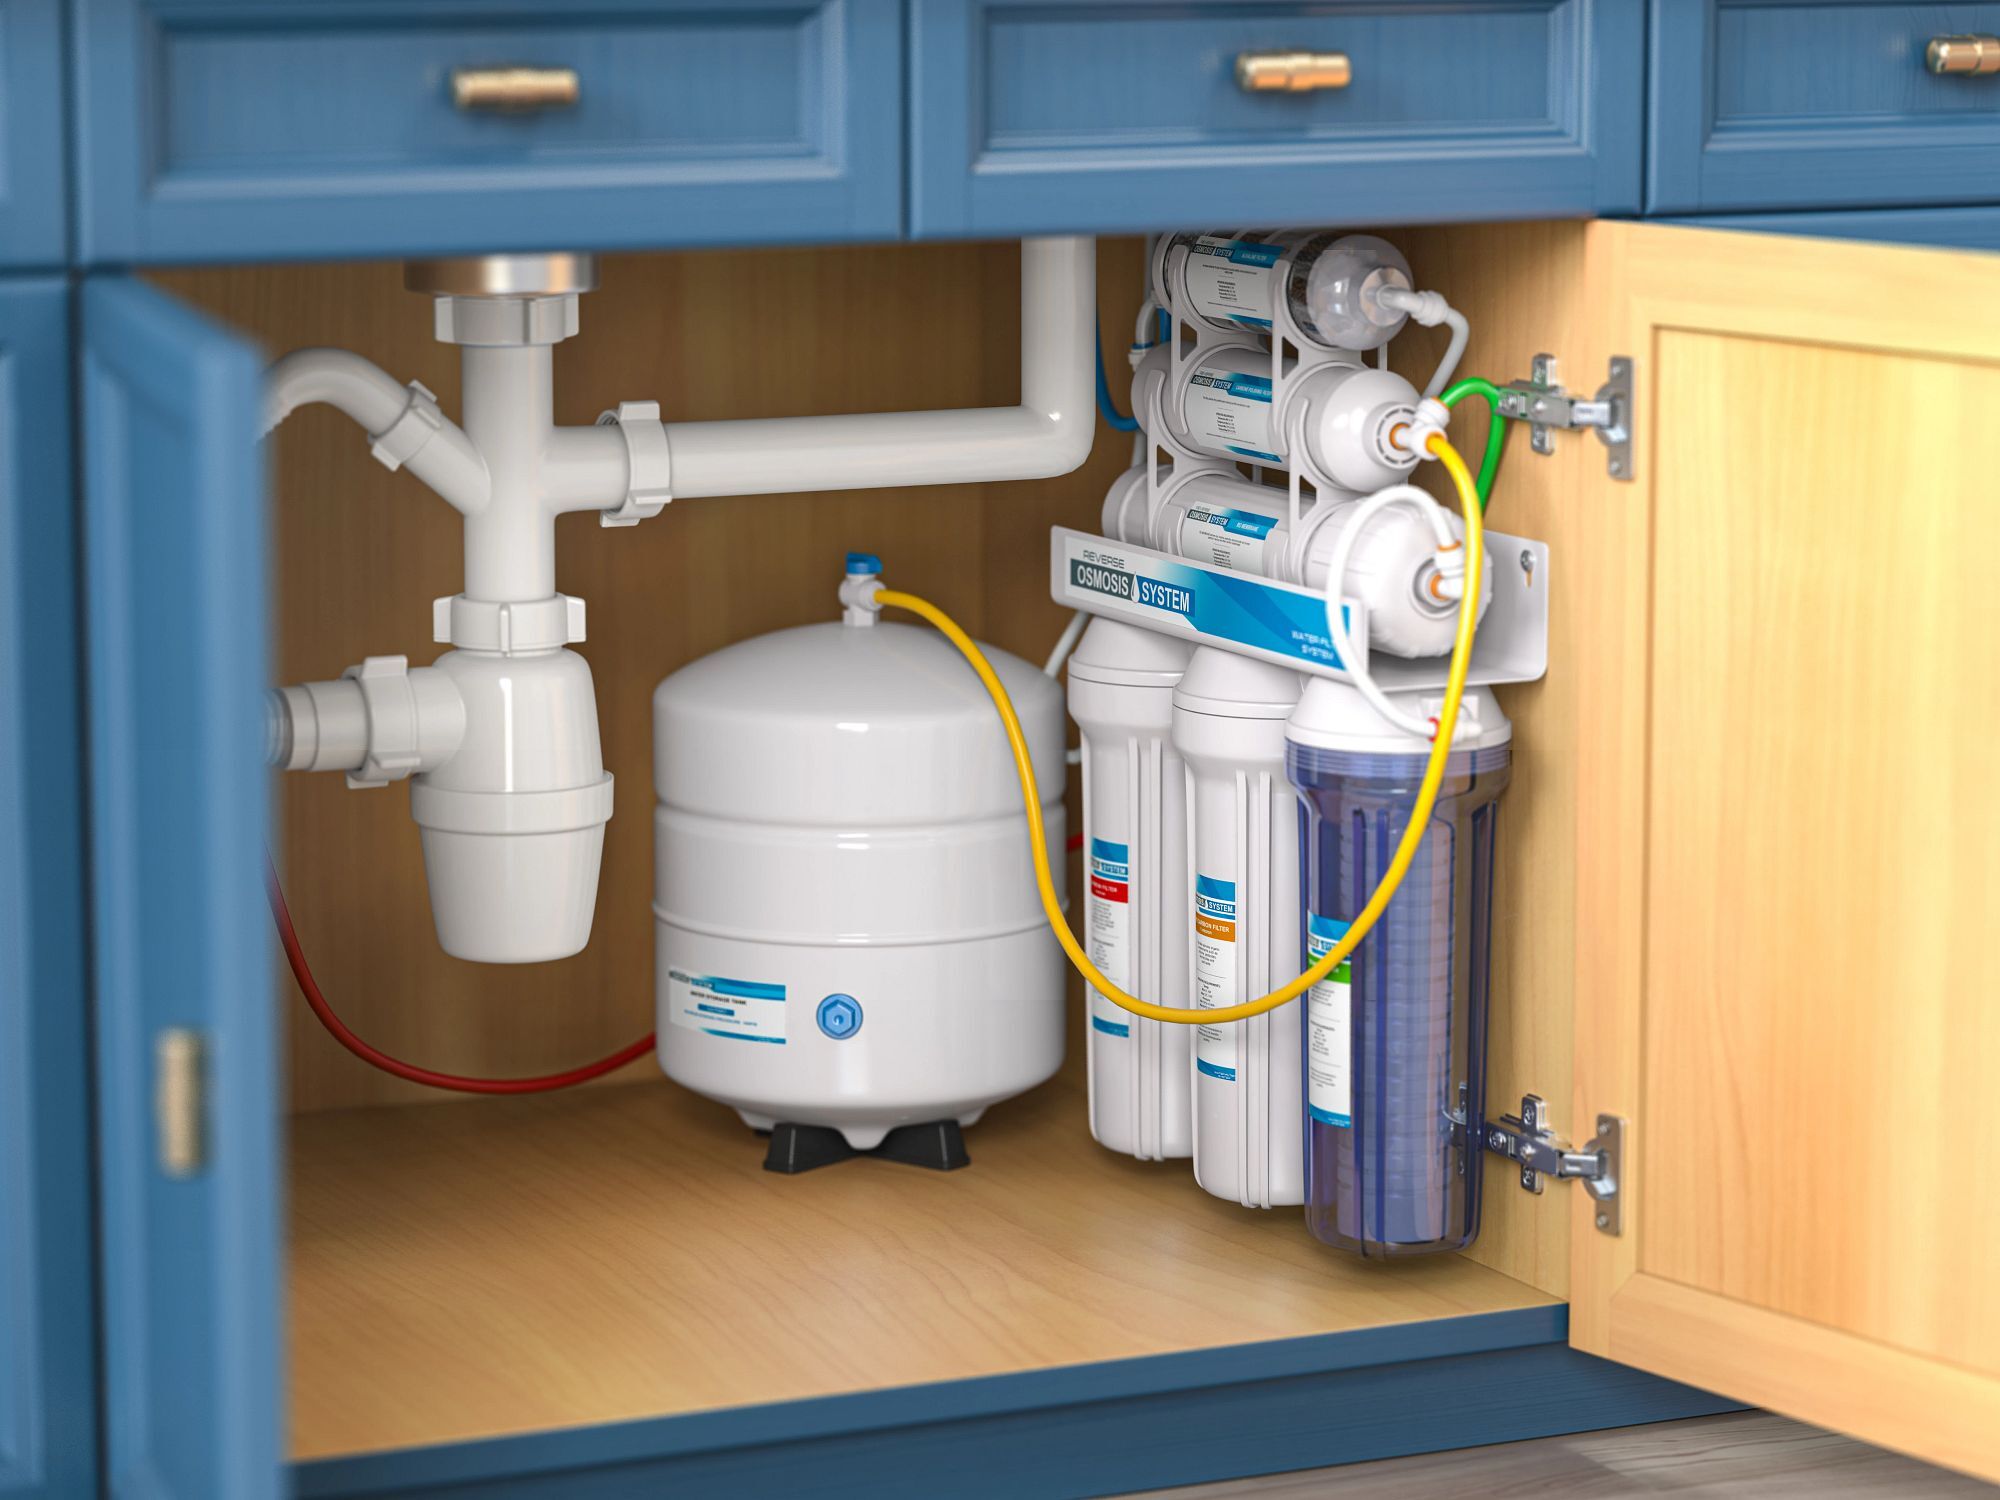
NSF Launches Protocol 549 for Glyphosate Reduction Claims
October 14, 2026P549 is the first standard globally that validates glyphosate reduction performance of water filtration systems and products.
Cambium Analytica, an NSF Company, Opens New Lab in Traverse City, Mich
October 6, 2026Ribbon cutting debuts innovative 15,000-square-foot testing facility to support evolving needs of the food & supplement industries.
NSF Drives Industry Conversations at SupplySide Global 2026 - Las Vegas, Oct. 26–30
September 17, 2026NSF returns to SupplySide Global with expert-led training and trusted certification solutions. Visit Booth 4741 to discover how NSF and Cambium Analytica help brands build trust, increase consumer confidence and stand out in a competitive marketplace.
NSF Welcomes Hanjun Kwon, Managing Director, APAC
September 14, 2026Experienced business leader to drive sustainable growth, organizational development and operational excellence across the Asia-Pacific region.